Cybersecurity

Latest Dispatches
Newest on top • 580 stories
Alpine Linux rebuilds GitLab after attempted RCE attack
Cybersecurity•3m read
BleepingComputer

Alpine Linux rebuilds GitLab after attempted RCE attack

Hackers attempted to exploit a critical GitLab vulnerability in Alpine Linux's development infrastructure on October 20 — 21, prompting the open-source project to rebuild its GitLab server and reset all passwords over concerns of a possible comprom...

BleepingComputerabout 3 hours ago

North Korea linked to massive Binance crypto heist
Cybersecurity•2m read
The Verge

North Korea linked to massive Binance crypto heist

The FBI says North Korea was behind the massive $6.3 billion crypto heist that hit Binance on October 29th. The FBI labeled the activity "TraderTraitor" and said that it had observed actors it has connected to hack converting the tokens to Ethereum a...

The Vergeabout 3 hours ago
Reddit to lock content behind logins to fight scrapers
Cybersecurity•3m read
BleepingComputer

Reddit to lock content behind logins to fight scrapers

Reddit announced in a post by co-founder Steve Huffman that the site will gradually become a "logged-in service," offering limited access to visitors without accounts. For the past 20 years, the discussion platform has let users browse almost all it...

BleepingComputerabout 24 hours ago

Behind the Scenes of How Operation Blackout Went Down
Cybersecurity•5m read
Dark Reading

Behind the Scenes of How Operation Blackout Went Down

Cybersecurity In-Depth: Feature articles on security strategy, latest trends, and people to know. A recent law enforcement operation to dismantle harmful scam centers was a big success. A threat intelligence expert walks us through what happened and...

Dark Reading2 days ago
Undead Software Projects Continue to Raise Security Risks
Cybersecurity•5m read
Dark Reading

Undead Software Projects Continue to Raise Security Risks

A security firm patched a decade-old app to prevent the takeover of millions of machines, highlighting that abandoned domains remain a boon to attackers. When managed security service provider Eye Security spotted an odd update process in a client's...

Dark Reading2 days ago
SS7 and Diameter Attacks: How Signaling Flaws Expose Your Phone
Cybersecurity•8m read
BleepingComputer

SS7 and Diameter Attacks: How Signaling Flaws Expose Your Phone

SS7 and Diameter signaling attacks can track, intercept, and impersonate you. Here's how they work and how to stop them. Your phone can be tracked, your SMS two-factor codes can be intercepted, and your number can be impersonated, all without malwar...

BleepingComputer2 days ago
Bulletproof Host Virtualine Loses Its Domain to FBI Seizure
Cybersecurity•2m read
SecurityWeek

Bulletproof Host Virtualine Loses Its Domain to FBI Seizure

The FBI has seized virtualine.net, the domain of a Russian-speaking bulletproof hosting services provider associated with various cybercriminal operations. According to court documents, Virtualine, also known as Secury, Massgod, Spamhouse, Lanedo, a...

SecurityWeek2 days ago

Passkeys Are Better Than Passwords. But They Are Not Enough.
Cybersecurity•5m read
SecurityWeek

Passkeys Are Better Than Passwords. But They Are Not Enough.

For decades, passwords have been one of cybersecurity's most persistent weaknesses. Users forget them, reuse them, share them, and surrender them to convincing phishing sites. Attackers steal credentials, automate credential stuffing, and increasingl...

SecurityWeek2 days ago
Top cybersecurity conferences to attend in 2027
Cybersecurity•4m read
Cybersecurity Dive

Top cybersecurity conferences to attend in 2027

As 2027 approaches, leaders and practitioners are preparing for a slate of cybersecurity conferences that could fill their calendars. Government officials, industry executives and security experts from around the world will convene throughout 2027 to...

Cybersecurity Dive2 days ago
Fresh WordPress Vulnerability in Attackers’ Crosshairs
Cybersecurity•2m read
SecurityWeek

Fresh WordPress Vulnerability in Attackers’ Crosshairs

Threat actors started exploiting a new high-severity WordPress vulnerability within hours of patches rolling out, Defiant warns. Patched on October 28 in WordPress 7.1.4, the security defect impacts the WordPress update process and can be exploited ...

SecurityWeek2 days ago
Why CTF Competitions May Be More Important Than Ever
Cybersecurity•9m read
Dark Reading

Why CTF Competitions May Be More Important Than Ever

Cybersecurity In-Depth: Feature articles on security strategy, latest trends, and people to know. As artificial intelligence squeezes early-career learning opportunities, capture-the-flag contests could be one way to help pick up the slack. Artific...

Dark Reading2 days ago

As Russia's Cyberwar Evolves, Belarus Steps Forward
Cybersecurity•4m read
Dark Reading

As Russia's Cyberwar Evolves, Belarus Steps Forward

Breaking cybersecurity news, news analysis, commentary, and other content from around the world, with an initial focus on the Middle East & Africa, the Asia Pacific, Europe, and Latin America. The "FrostyNeighbor" advanced persistent threat (APT) la...

Dark Reading2 days ago
Microsoft finally fixes VPN issues caused by September updates
Cybersecurity•3m read
BleepingComputer

Microsoft finally fixes VPN issues caused by September updates

Microsoft has resolved Always On VPN connection failures triggered after installing the September 2026 Windows 11 security updates. The Always On VPN remote access solution runs in the background and establishes secure tunnels back to the user's cor...

BleepingComputer2 days ago
CISA says max severity GitLab flaw now exploited in the wild
Cybersecurity•3m read
BleepingComputer

CISA says max severity GitLab flaw now exploited in the wild

Attackers have started exploiting a maximum-severity GitLab vulnerability patched earlier this month, according to the US Cybersecurity and Infrastructure Security Agency (CISA). Tracked as CVE-2026-97229, this critical security flaw was discovered ...

BleepingComputer2 days ago
What we know so far about the Binance hack
Cybersecurity•5m read
BBC News Technology

What we know so far about the Binance hack

- Published Binance, the world's largest crypto exchange, has been hit by what is believed to be the largest crypto hack ever at $6.3bn (£4.7bn). Crypto is a type of digital asset which does not exist physically like cash or coins. Instead, people ...

BBC News Technology2 days ago
Binance probes potential $5.8 billion crypto-theft hack
Cybersecurity•3m read
BleepingComputer

Binance probes potential $5.8 billion crypto-theft hack

Cryptocurrency exchange Binance is investigating a potential security breach involving up to $5.8 billion in digital assets, in what could become the largest cryptocurrency hack in history. If confirmed stolen, the amount would far exceed the $1.5 b...

BleepingComputer3 days ago
Rethinking Cybersecurity Awareness in the AI Era
Cybersecurity•14m read
Dark Reading

Rethinking Cybersecurity Awareness in the AI Era

Cybersecurity In-Depth: Feature articles on security strategy, latest trends, and people to know. This installment of the Reporters' Notebook video series discusses some of the trends and topics from Cybersecurity Awareness Month, from using AI for ...

Dark Reading3 days ago
Anthropic-Themed Phishing Emails Bypass Top Security Tools
Cybersecurity•5m read
Dark Reading

Anthropic-Themed Phishing Emails Bypass Top Security Tools

Obvious phishing emails with numerous red flags are somehow getting past some of the industry-leading secure email gateway (SEG) products. Attackers are managing to sneak low-grade phishing emails through brand name email security products, as evide...

Dark Reading3 days ago
Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities
Cybersecurity•2m read
SecurityWeek

Adobe, Veeam, Juniper Networks Patch Critical Vulnerabilities

Adobe, Veeam, and Juniper Networks have released patches for over three dozen vulnerabilities across their products, including multiple critical-severity code execution flaws. This week, Adobe fixed 12 vulnerabilities in Campaign Classic, Connect, C...

SecurityWeek3 days ago
Threat Modeling With 4 Simple Questions on a White Board
Cybersecurity•6m read
Dark Reading

Threat Modeling With 4 Simple Questions on a White Board

A four-question exercise that CISOs can use to create a threat model that promises results, without a big spend. ISC2 Strategic Congress 2026 — Denver — A threat model should be a starting organizing principle for any security program. But r...

Dark Reading3 days ago
Fake crypto app on Apple App Store linked to $23K wallet theft
Cybersecurity•4m read
BleepingComputer

Fake crypto app on Apple App Store linked to $23K wallet theft

A fake cryptocurrency trading app called Padre Terminal, previously available on the Apple App Store for iOS devices, has been linked to the theft of approximately $23,000 from 27 Solana wallets. Blockchain investigator Iris confirmed that one victi...

BleepingComputer3 days ago
HHS Filing Puts iRhythm Data Breach Toll at 8.2 Million
Cybersecurity•2m read
SecurityWeek

HHS Filing Puts iRhythm Data Breach Toll at 8.2 Million

More than 8 million people were impacted by a June 2026 data breach at medical equipment provider iRhythm. The company, which specializes in wearable cardiac monitoring technology and is best known for its Zio wearable ECG monitor, disclosed the inc...

SecurityWeek3 days ago
Over 41,000 DHS Employee Records Leaked Online
Cybersecurity•2m read
SecurityWeek

Over 41,000 DHS Employee Records Leaked Online

A threat actor has leaked online a database containing the personal and work information of thousands of US Department of Homeland Security employees. The hacker, who uses the handle Department of Peace, has leaked more than 41,000 records. "They ha...

SecurityWeek3 days ago
Windows 11 KB5127936 update released with 41 changes and fixes
Cybersecurity•4m read
BleepingComputer

Windows 11 KB5127936 update released with 41 changes and fixes

Microsoft released the KB5127936 preview cumulative update for Windows 11 versions 25H2 and 26H2, with 41 changes, including File Explorer and Cloud rebuild improvements. KB5127936 is a preview update that adds new features and fixes at the end of e...

BleepingComputer3 days ago
New Cisco firewall zero-day exploited to crash SSL VPN devices
Cybersecurity•3m read
BleepingComputer

New Cisco firewall zero-day exploited to crash SSL VPN devices

Cisco released security updates to patch a denial-of-service zero-day in Adaptive Security Appliance (ASA) and Threat Defense (FTD) software that attackers are exploiting to remotely crash vulnerable firewall devices. Tracked as CVE-2026-76418, this...

BleepingComputer3 days ago
Cyber Vulnerabilities Besiege Italy, Absent Clear Cause
Cybersecurity•7m read
Dark Reading

Cyber Vulnerabilities Besiege Italy, Absent Clear Cause

Breaking cybersecurity news, news analysis, commentary, and other content from around the world, with an initial focus on the Middle East & Africa, the Asia Pacific, Europe, and Latin America. Researchers can't quite explain why cyber threats look s...

Dark Reading3 days ago
Discord to let search engines index public server messages
Cybersecurity•3m read
BleepingComputer

Discord to let search engines index public server messages

Discord will allow search engines to index discussions in Discoverable Servers and make them accessible on the web to users outside the platform without an account or invitation. The goal is to surface useful information to the wider internet commun...

BleepingComputer4 days ago
Hackers now scanning systems for recently-patched Oracle flaw
Cybersecurity•3m read
BleepingComputer

Hackers now scanning systems for recently-patched Oracle flaw

Attackers have begun probing the Internet for systems unpatched against a recently disclosed critical Oracle E-Business Suite (EBS) vulnerability. Discovered in a core component of EBS's Application Object Library and tracked as CVE-2026-101767, thi...

BleepingComputer4 days ago
Microsoft urges Entra ID admins to migrate users to passkeys
Cybersecurity•3m read
BleepingComputer

Microsoft urges Entra ID admins to migrate users to passkeys

Microsoft again asked Entra ID administrators to migrate users to phishing-resistant methods to avoid sign-in disruptions before it retires SMS and voice authentication in February 2027. This retirement process applies only to Microsoft Entra ID wor...

BleepingComputer4 days ago
Chrome and Firefox Updates Patch Over 200 Vulnerabilities
Cybersecurity•2m read
SecurityWeek

Chrome and Firefox Updates Patch Over 200 Vulnerabilities

Google and Mozilla on Tuesday rolled out fresh Chrome and Firefox updates that resolve more than 200 vulnerabilities in the popular browsers. The Chrome 156 update arrives with patches for 52 security defects, including four critical-severity flaws:...

SecurityWeek4 days ago
China-Linked Hackers Exploit PHP2Shell to Root Firewalls
Cybersecurity•3m read
SecurityWeek

China-Linked Hackers Exploit PHP2Shell to Root Firewalls

A China-linked threat actor has been exploiting the PHP2Shell vulnerabilities to gain root access to firewalls and deploy webshells for persistent access, cybersecurity firm Dream reports. The hackers have been chaining an exploit for the two PHP fl...

SecurityWeek4 days ago
SBOMs Alone Can't Reveal the Scope of a Supply Chain Attack
Cybersecurity•4m read
Dark Reading

SBOMs Alone Can't Reveal the Scope of a Supply Chain Attack

A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises. ISC2 Strategic Congress 2026 — Denver — Depending on a software bill of materials (SBOM) ...

Dark Reading4 days ago
External Teams Chats Anchor 15-Minute Malware Delivery
Cybersecurity•5m read
Dark Reading

External Teams Chats Anchor 15-Minute Malware Delivery

Main bombing sis getting a new look with a wide-scale, ongoing social engineering campaign that might be tied to the Black Basta ransomware gang. Threat actors are abusing Microsoft Teams' external chat functionality at scale, using IT-support imper...

Dark Reading4 days ago
Brotli bug reaches far beyond Node.js (CVE-2026-111497)
Cybersecurity•3m read
Help Net Security

Brotli bug reaches far beyond Node.js (CVE-2026-111497)

A vulnerability in Brotli, Google's widely used open-source compression library, is putting a broad range of software at risk. ### About CVE-2026-111497 Alternatively known as "Node2Shell", "Broccoli2Shell" and "Brotli2Shell", CVE-2026-111497 is a ...

Help Net Security4 days ago
UNM Health ransomware attack disrupts patient care, surgeries
Cybersecurity•4m read
BleepingComputer

UNM Health ransomware attack disrupts patient care, surgeries

The University of New Mexico Health Sciences Center disclosed a cyberattack that caused system outages and disrupted patient care and academic activities. On Monday, UNM Health, the university's healthcare provider, began temporarily limiting new pa...

BleepingComputer4 days ago
HPE Patches Dozens of Critical Flaws in Networking Products
Cybersecurity•2m read
SecurityWeek

HPE Patches Dozens of Critical Flaws in Networking Products

HPE last week released patches for 72 vulnerabilities in the AOS-8 and AOS-10 wireless operating systems of its Aruba networking products, including 33 critical-severity flaws. The security updates address eight max-severity bugs: CVE-2026-79844, CV...

SecurityWeek5 days ago
Energy giant ENGIE discloses data breach affecting customers
Cybersecurity•2m read
BleepingComputer

Energy giant ENGIE discloses data breach affecting customers

French energy giant ENGIE, one of the world's largest power and natural gas providers, confirmed that attackers stole customer data after breaching a marketing platform used by business partners. ENGIE operates in renewable energy, infrastructure, a...

BleepingComputer5 days ago
Apple backports CoreGraphics zero-day patches to older iPhones
Cybersecurity•2m read
BleepingComputer

Apple backports CoreGraphics zero-day patches to older iPhones

Apple has backported security patches released last month to older iPhones and iPads, addressing a zero-day bug exploited in "extremely sophisticated" targeted attacks on iOS devices. Apple patched the same vulnerability in September for devices run...

BleepingComputer5 days ago
Tailscale warns of SSH flaws allowing root privilege escalation
Cybersecurity•5m read
BleepingComputer

Tailscale warns of SSH flaws allowing root privilege escalation

The Tailscale security team is working to patch almost a dozen security vulnerabilities that could be exploited to steal credentials, crash servers, gain root privileges, and more. Tailscale develops a software-defined mesh virtual private network (...

BleepingComputer5 days ago
DreamHost forces password resets in ongoing "incident"
Cybersecurity•3m read
BleepingComputer

DreamHost forces password resets in ongoing "incident"

DreamHost has forced password resets for email and FTP/SFTP users following an incident that disrupted connections to the File Manager interface. The latest update from the web hosting provider notes that all affected account owners have received re...

BleepingComputer6 days ago
10 Software Security Practices Built for the Next 250 Years
Cybersecurity•5m read
Dark Reading

10 Software Security Practices Built for the Next 250 Years

This Cybersecurity Awareness Month's theme, "Securing the Next 250," asks us to look beyond vulnerabilities and consider what will make our digital systems resilient for generations. ### OPINION When I testified before Congress with my L0pht collea...

Dark Reading6 days ago
'Gheist' Weaponizes GitHub Tokens to Steal Cloud Secrets
Cybersecurity•5m read
Dark Reading

'Gheist' Weaponizes GitHub Tokens to Steal Cloud Secrets

An ongoing supply chain attack is harvesting credentials and sensitive data from thousands of developer repositories. An ongoing attack is abusing compromised GitHub tokens to harvest cloud secrets and credentials from thousands of developer reposit...

Dark Reading6 days ago
CISA promises proactive defense in new strategic plan
Cybersecurity•6m read
Cybersecurity Dive

CISA promises proactive defense in new strategic plan

The Cybersecurity and Infrastructure Security Agency on Monday laid out an ambitious vision for protecting U.S. government networks and critical infrastructure systems over the next four years. The "CISA 2030: Defend, Harden, Prevail" strategy chart...

Cybersecurity Dive6 days ago
PwC confirms learning records breached in attack on vendor site
Cybersecurity•1m read
Cybersecurity Dive

PwC confirms learning records breached in attack on vendor site

PwC on Monday said it was investigating claims that hackers had breached a third-party vendor site the company uses to house employee learning records. The company disclosed the breach amid claims from Everest ransomware that it had stolen 590 gigab...

Cybersecurity Dive6 days ago
The PHP Meltdown Shows How AI Makes Bugs More Exploitable
Cybersecurity•4m read
Wired Security

The PHP Meltdown Shows How AI Makes Bugs More Exploitable

Welcome to Kernel Panic, a weekly newsletter by Lily Hay Newman and Matt Burgess from inside the new world of privacy and digital security. To receive this newsletter in your inbox each week, sign up here. As security teams and web admins scrambled ...

Wired Security6 days ago
PHP2Shell security flaws now sucessfully exploited in the wild
Cybersecurity•3m read
BleepingComputer

PHP2Shell security flaws now sucessfully exploited in the wild

Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild. The malicious activity was caught by Adel Karimi, detection and response lead at Perplexity, who...

BleepingComputer6 days ago
Kali Linux 2026.3 released with 6 new tools, desktop updates
Cybersecurity•4m read
BleepingComputer

Kali Linux 2026.3 released with 6 new tools, desktop updates

Kali Linux has released version 2026.3, its third release this year, featuring six new hacking tools, desktop environment improvements, refreshed build scripts, and more. This Linux distribution is available as an installable OS or as a live environ...

BleepingComputer6 days ago
Genesys Hack Exposes Customer Data From Internal Systems
Cybersecurity•2m read
SecurityWeek

Genesys Hack Exposes Customer Data From Internal Systems

Customer experience company Genesys says it has contained a cyberattack that involved unauthorized access to data. Headquartered in Menlo Park, California, Genesys is a provider of customer experience and call center technology for mid-sized and lar...

SecurityWeek6 days ago
PHP2Shell Exploitation Moves From Probes to Working Shells
Cybersecurity•2m read
SecurityWeek

PHP2Shell Exploitation Moves From Probes to Working Shells

Attackers have successfully exploited the PHP2Shell vulnerabilities to run shell commands on honeypot servers, a researcher reported over the weekend. Tracked as CVE-2026-109618 and CVE-2026-109619, the critical PHP2Shell flaws can be exploited for ...

SecurityWeek6 days ago
953 Online Stores Infected in Long-Lasting Malware Campaign
Cybersecurity•3m read
SecurityWeek

953 Online Stores Infected in Long-Lasting Malware Campaign

A threat actor has infected 953 online stores, most of them running Magento, with loader code as part of a long-running campaign, cybersecurity firm Sansec reports. The attacks have been ongoing since July 2025, and the threat actor has used five di...

SecurityWeek6 days ago
Exposed to PHP2Shell? Cyber Experts Weigh in With Advice
Cybersecurity•8m read
Dark Reading

Exposed to PHP2Shell? Cyber Experts Weigh in With Advice

Fixing the critical PHP flaws is not as simple as clicking "Update." Here's how to assess your risk, and what you can do to protect yourself. New data shows that organizations aren't moving to patch PHP2Shell as fast as attackers are moving to explo...

Dark Reading9 days ago
Capcom data breach exposes 11.7 million account records
Cybersecurity•3m read
Help Net Security

Capcom data breach exposes 11.7 million account records

Players who signed up for Capcom's online account service may want to look twice at emails that seem to come from the company. The company has disclosed that a third party gained unauthorized access to customer information linked to CAPCOM ID, the a...

Help Net Security9 days ago
UK proposes 14-year jail terms for subsea cable saboteurs
Cybersecurity•3m read
Help Net Security

UK proposes 14-year jail terms for subsea cable saboteurs

Damaging a cable on the seabed off the UK coast could soon cost someone 14 years of their life behind bars, under plans the British government published this week. The proposal comes from a White Paper by the Department for Digital, Culture, Media a...

Help Net Security9 days ago
PHP shares mitigation for new RCE vulnerability with no patch
Cybersecurity•3m read
BleepingComputer

PHP shares mitigation for new RCE vulnerability with no patch

The PHP security team has shared mitigation measures for a new remote code execution vulnerability that affects systems with non-default configurations and has no patch. PHP is an open-source web development language used by nearly 70% of all websit...

BleepingComputer9 days ago
Quest Diagnostics confirms data breach exposed patient records
Cybersecurity•3m read
BleepingComputer

Quest Diagnostics confirms data breach exposed patient records

American clinical laboratory company Quest Diagnostics disclosed that patient records have been exposed after a threat actor gained unauthorized access to its Quanum LSM system. The company learned about the breach on October 21 and deployed its inc...

BleepingComputer9 days ago
Why Caribbean Threats Cascade Into Global Cyber-Risk
Cybersecurity•4m read
Dark Reading

Why Caribbean Threats Cascade Into Global Cyber-Risk

Breaking cybersecurity news, news analysis, commentary, and other content from around the world, with an initial focus on the Middle East & Africa, the Asia Pacific, Europe, and Latin America. The region is demonstrating what happens when exploits a...

Dark Reading9 days ago
China APT Uses AI Pentest Tool Artex in ConnectWise Attacks
Cybersecurity•3m read
SecurityWeek

China APT Uses AI Pentest Tool Artex in ConnectWise Attacks

A China-linked threat actor has been using the open source AI penetration testing framework Artex to automate a recent ConnectWise hacking campaign targeting hundreds of organizations, Microsoft reports. Tracked as Storm-0940 and active since at lea...

SecurityWeek9 days ago
Attackers Exploit Third Arista VCO Zero-Day in Four Months
Cybersecurity•2m read
SecurityWeek

Attackers Exploit Third Arista VCO Zero-Day in Four Months

Networking solutions provider Arista Networks on Thursday rolled out patches for an exploited zero-day vulnerability in its centralized management tool VeloCloud Orchestrator (VCO). The critical-severity security defect is tracked as CVE-2026-114625...

SecurityWeek9 days ago
Cyber Insurance's New Reality: Underwriting Isn't Enough
Cybersecurity•6m read
Dark Reading

Cyber Insurance's New Reality: Underwriting Isn't Enough

Rising AI, social engineering, and cloud risks are pushing carriers beyond risk transfer and deeper into cybersecurity itself. The relentless evolution of the threat landscape has pushed cyber insurance companies to follow suit with a continuous exp...

Dark Reading9 days ago
HPE patches eight max severity RCE and auth bypass AOS flaws
Cybersecurity•3m read
BleepingComputer

HPE patches eight max severity RCE and auth bypass AOS flaws

Hewlett Packard Enterprise (HPE) released security updates to patch 72 vulnerabilities in the Aruba Operating System (ArubaOS), including eight maximum-severity authentication bypass and code execution issues. Also known as AOS, ArubaOS powers Aruba...

BleepingComputer9 days ago
11 Million Impacted by Capcom Data Breach
Cybersecurity•2m read
SecurityWeek

11 Million Impacted by Capcom Data Breach

Japanese gaming company Capcom has disclosed a data breach impacting 11 million email addresses and the personal information of a small number of individuals. The incident, the gaming giant says, was discovered on October 19 and involved unauthorize...

SecurityWeek9 days ago
State Bank of India Suffers a Customer PII Data Leak
Cybersecurity•6m read
Dark Reading

State Bank of India Suffers a Customer PII Data Leak

Breaking cybersecurity news, news analysis, commentary, and other content from around the world, with an initial focus on the Middle East & Africa, the Asia Pacific, Europe, and Latin America. Relatively small data breaches in India can turn quite s...

Dark Reading9 days ago
Railway warns devs to rotate secrets after potential breach
Cybersecurity•2m read
BleepingComputer

Railway warns devs to rotate secrets after potential breach

Cloud hosting provider Railway published an urgent warning to users after detecting suspicious activity on its systems that store customer environment variables earlier this week. The company says its investigation indicates that, in some cases, an ...

BleepingComputer10 days ago
Capcom confirms data breach affecting 11.7 million accounts
Cybersecurity•3m read
BleepingComputer

Capcom confirms data breach affecting 11.7 million accounts

Japanese gaming giant Capcom has confirmed that hackers breached its membership service, CAPCOM ID, exposing more than 11.7 million customer email addresses and associated information. Apart from emails, exposed data includes account creation date, ...

BleepingComputer10 days ago
Hacker Conversations: Corey Thuen and the Evil Bit
Cybersecurity•11m read
SecurityWeek

Hacker Conversations: Corey Thuen and the Evil Bit

Corey Thuen is a hacker with a hacker mindset that is focused on the right way to do wrong things to get the right result. Corey Thuen is the founder and CEO of Gravwell, a firm with a slight difference: it develops data analytics and vulnerability ...

SecurityWeek10 days ago
Signal Vulnerability Lets Malicious Callers Block Hang-Ups
Cybersecurity•2m read
SecurityWeek

Signal Vulnerability Lets Malicious Callers Block Hang-Ups

Signal has resolved a critical-severity vulnerability that could allow a malicious caller to keep audio and video tracks enabled even after the user hung up. The security defect is tracked as CVE-2026-113380 (CVSS score of 9.3) and impacts RingRTC, ...

SecurityWeek10 days ago
Amazon says PHP2Shell exploitation began 4 days before patches
Cybersecurity•3m read
BleepingComputer

Amazon says PHP2Shell exploitation began 4 days before patches

Security researchers at Amazon Threat Intelligence say attackers began targeting the PHP2Shell flaws four days before security patches were released on Wednesday. Tracked as CVE-2026-109618 and CVE-2026-109619, the two critical vulnerabilities let a...

BleepingComputer10 days ago
Microsoft shares how to fix broken Exchange Online EWS apps
Cybersecurity•3m read
BleepingComputer

Microsoft shares how to fix broken Exchange Online EWS apps

Microsoft says IT admins can re-enable the retired Exchange Web Services (EWS) API in Exchange Online to fix EWS apps that have stopped working. EWS is an API for developing apps that can access Exchange mailbox items (e.g., email messages, meetings...

BleepingComputer10 days ago
GitLab warns of new max severity code execution vulnerability
Cybersecurity•3m read
BleepingComputer

GitLab warns of new max severity code execution vulnerability

GitLab has released security patches for a maximum-severity Regular Expression Compiler flaw that can let remote attackers run arbitrary code on vulnerable servers. This security issue is tracked as CVE-2026-110264 and was reported by a security res...

BleepingComputer10 days ago
Authorities disrupt nearly 11,000 cybercrime networks in Africa
Cybersecurity•3m read
BleepingComputer

Authorities disrupt nearly 11,000 cybercrime networks in Africa

Law enforcement agencies have disrupted nearly 11,000 cybercriminal networks and arrested more than 1,400 people in Operation Serengeti III, which targeted business email compromise, ransomware, and online scams. Coordinated by Interpol, the operati...

BleepingComputer10 days ago
PHP2Shell Exploitation Started Days Before Patches
Cybersecurity•5m read
SecurityWeek

PHP2Shell Exploitation Started Days Before Patches

Threat actors started probing for servers affected by two critical remote code execution (RCE) vulnerabilities in PHP four days before the fixes, Amazon reports. Patches for the two flaws, known as PHP2Shell and tracked as CVE-2026-109618 and CVE-20...

SecurityWeek10 days ago
Cisco Patches 34 Vulnerabilities Across Multiple Products
Cybersecurity•2m read
SecurityWeek

Cisco Patches 34 Vulnerabilities Across Multiple Products

Cisco on Wednesday announced patches for 34 vulnerabilities across Expressway Series, IOS XR, Snort 3, and Unified Communications products. Expressway Series received fixes for 10 vulnerabilities, including a critical-severity remote code execution ...

SecurityWeek10 days ago
Splunk, SolarWinds Release Fresh Security Updates
Cybersecurity•2m read
SecurityWeek

Splunk, SolarWinds Release Fresh Security Updates

Splunk and SolarWinds this week released patches for multiple vulnerabilities, including flaws leading to code execution, privilege escalation, denial-of-service (DoS), and information disclosure. On Wednesday, Splunk rolled out security updates for...

SecurityWeek10 days ago
'PHP2Shell' Bugs Signal Red Alert for Security Industry
Cybersecurity•5m read
Dark Reading

'PHP2Shell' Bugs Signal Red Alert for Security Industry

Security teams are scrambling to remediate two critical PHP vulnerabilities following leaked details and reports of exploitation attempts. A pair of critical vulnerabilities tied to open source scripting language PHP appear to have significant conse...

Dark Reading11 days ago
TiDB Breach Exposes Flawed Cloud Security Assumptions
Cybersecurity•6m read
Dark Reading

TiDB Breach Exposes Flawed Cloud Security Assumptions

Cloud providers may be storing sensitive customer data, without either party knowing it. But when a provider is breached, the data comes home to roost. A breach of an open source database provider may have inadvertently highlighted a serious gap in ...

Dark Reading11 days ago
Chrome puts insecure sites behind a permission prompt
Cybersecurity•3m read
Help Net Security

Chrome puts insecure sites behind a permission prompt

Google has rolled out a change to Chrome that asks users for permission before making an insecure HTTP connection. The protection is now enabled by default for all users, following its introduction earlier this year for users of Safe Browsing's Enhan...

Help Net Security11 days ago
PHP ships emergency patches for critical PHP2Shell flaws
Cybersecurity•4m read
BleepingComputer

PHP ships emergency patches for critical PHP2Shell flaws

The PHP security team released emergency security patches for two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618 and CVE-2026-109619) tracked collectively as PHP2Shell. The two unauthenticated RCE flaws were discovered by Cali...

BleepingComputer11 days ago
Widespread PHP Flaw May Cause Many Site Outages Today
Cybersecurity•3m read
Krebs on Security

Widespread PHP Flaw May Cause Many Site Outages Today

Expect to see quite a few websites serving error pages today: Nearly 70 percent of websites need to update their core software to fix a pair of vulnerabilities that allow an attacker to seize full control over affected servers. Experts say there are ...

Krebs on Security11 days ago
OVHcloud GitHub Compromise Tied to GlassWorm Threat Actors
Cybersecurity•5m read
Dark Reading

OVHcloud GitHub Compromise Tied to GlassWorm Threat Actors

A developer's GitHub account that was compromised several months earlier was used to push malicious code to unsuspecting users. GlassWorm threat actors appear to have snagged a big fish. French cloud provider OVHcloud on Monday disclosed that one o...

Dark Reading11 days ago
Microsoft PowerToys adds CursorHide, Button Lock mouse tools
Cybersecurity•3m read
BleepingComputer

Microsoft PowerToys adds CursorHide, Button Lock mouse tools

Microsoft has released PowerToys 0.102, with two new mouse utilities, new command-line tools, and Command Palette improvements. Mouse Button Lock, one of the new mouse tools, makes it easier to select items on screen by locking a mouse button while ...

BleepingComputer11 days ago
Microsoft says October updates didn’t actually fix VPN issues
Cybersecurity•3m read
BleepingComputer

Microsoft says October updates didn’t actually fix VPN issues

Microsoft says it mistakenly flagged a bug causing Always On VPN connection issues as fixed in the October 2026 Windows 11 cumulative updates. Always On VPN replaced the legacy DirectAccess technology and supports domain-joined, non-domain-joined, a...

BleepingComputer11 days ago
Decades-Old Windows Utility Powers Modern ClickFix Attack
Cybersecurity•4m read
Dark Reading

Decades-Old Windows Utility Powers Modern ClickFix Attack

The attack uses malicious Google search results related to Amazon and leverages the 'finger' utility to launch a CAPTCHA that installs malware, including the Lumma stealer. A new ClickFix attack is leveraging a legacy Window utility to run malicious...

Dark Reading11 days ago
PHP warns it plans to release 2 emergency patches imminently
Cybersecurity•2m read
Ars Technica

PHP warns it plans to release 2 emergency patches imminently

Website admins, brace yourselves. Fixes for what are believed to be uncommonly severe vulnerabilities are scheduled to drop in a little more than 12 hours for PHP, a programming language that powers websites and Web applications everywhere. PHP main...

Ars Technica11 days ago
Stolen UpdraftCentral keys used to backdoor WordPress sites
Cybersecurity•4m read
BleepingComputer

Stolen UpdraftCentral keys used to backdoor WordPress sites

A threat actor breached TeamUpdraft's website, a developer of popular WordPress backup and security plugins, potentially compromising UpdraftCentral connection keys that can send commands to connected websites. TeamUpdraft detected unauthorized acce...

BleepingComputer11 days ago
Ahold Delhaize Restoring Services Disrupted by Cyberattack
Cybersecurity•2m read
SecurityWeek

Ahold Delhaize Restoring Services Disrupted by Cyberattack

Dutch-Belgian grocery giant Ahold Delhaize has restored some of the services impacted by last week's cyberattack and expects more to come back online within days. On October 12, the company took its systems offline in response to "a security issue" ...

SecurityWeek12 days ago
Zeabur shutting down after second security breach in two months
Cybersecurity•3m read
BleepingComputer

Zeabur shutting down after second security breach in two months

Development platform Zeabur has disclosed details of a cybersecurity incident in which an attacker used leaked internal credentials stored in plaintext to compromise its infrastructure and steal over 3.2 million environment variable records and infor...

BleepingComputer12 days ago
Incomplete security patches show hackers where to look next
Cybersecurity•3m read
Help Net Security

Incomplete security patches show hackers where to look next

Security patches are turning into roadmaps for attackers, with a growing share of fixes later found incomplete or open to bypass. Oren Yomtov, a security researcher at Terra Security, began tracking broken fixes after the team kept running into them...

Help Net Security12 days ago
Chrome flags malicious commands that scammers pass off as fixes
Cybersecurity•3m read
Help Net Security

Chrome flags malicious commands that scammers pass off as fixes

Google is updating Chrome's Enhanced Protection mode to detect scam websites and warn users when a page tricks them into copying a malicious command. The company introduced Enhanced Protection for Chrome's Safe Browsing feature in 2020 to address on...

Help Net Security12 days ago
CJIS v6.1 Compliance: 5 Practical Priorities for Agencies
Cybersecurity•5m read
BleepingComputer

CJIS v6.1 Compliance: 5 Practical Priorities for Agencies

For agencies responsible for protecting Criminal Justice Information (CJI), meeting CJIS requirements means more than putting security controls in place. Those controls need to work across the systems staff use every day, and agencies need to be able...

BleepingComputer12 days ago
Windows Server 2025 gets support for quick machine recovery
Cybersecurity•3m read
BleepingComputer

Windows Server 2025 gets support for quick machine recovery

Microsoft announced that IT administrators can now use quick machine recovery on Windows Server 2025 after installing the October 2026 security update. Quick machine recovery (QMR) lets IT admins fix critical boot failures with targeted Windows Upda...

BleepingComputer12 days ago
Hacker gets 8 years for stealing $3.3 million from taxpayers
Cybersecurity•3m read
BleepingComputer

Hacker gets 8 years for stealing $3.3 million from taxpayers

A Nigerian national was sentenced to eight years in prison for his involvement in a series of spearphishing attacks targeting US tax preparation businesses since 2019. 40-year-old Chukwuemeka Victor Amachukwu (also known as Chukwuemeka Victor Eletuo...

BleepingComputer12 days ago
Revolut outage disrupts online banking operations worldwide
Cybersecurity•2m read
BleepingComputer

Revolut outage disrupts online banking operations worldwide

Fintech company Revolut is working to resolve a massive outage that disrupted most of its services worldwide earlier today. Since the incident began, thousands of users on the Downdetector outage tracking platform have reported issues with the Revol...

BleepingComputer12 days ago
Hackers Steal 1.8 Million Records From Nikkei
Cybersecurity•2m read
SecurityWeek

Hackers Steal 1.8 Million Records From Nikkei

Japanese media giant Nikkei has disclosed a fresh data breach impacting more than 1.8 million records. According to the company, best known for major financial publications, including The Nikkei and Financial Times, the incident involved a cloud ser...

SecurityWeek12 days ago
Mastercard helps banks assess stablecoin risks before funds move
Cybersecurity•4m read
Help Net Security

Mastercard helps banks assess stablecoin risks before funds move

Mastercard has announced Stablecoin Security, a new risk intelligence solution, with Borderless.xyz and Keyrails as initial partners. As stablecoins play a growing role in cross-border and business-to-business payments, financial institutions need a ...

Help Net Security12 days ago
WordPress SEO plugin Rank Math compromised to backdoor websites
Cybersecurity•4m read
BleepingComputer

WordPress SEO plugin Rank Math compromised to backdoor websites

Some downloads of the Rank Math PRO WordPress plugin from the vendor's official website carried malware that planted hidden backdoors in a supply-chain attack last week. According to the vendor, a limited number of users who downloaded version 3.0.1...

BleepingComputer13 days ago
OnlyFans Copyright Takedowns Expose Compromised Websites
Cybersecurity•16m read
Dark Reading

OnlyFans Copyright Takedowns Expose Compromised Websites

Copyright takedown requests tied to OnlyFans and other adult content creators are revealing how attackers exploit vulnerable university and government websites to manipulate search results. UpGuard's Greg Pollock explains what universities, governmen...

Dark Reading13 days ago
Researchers Infiltrate Microsoft Tech Support Scam Operation
Cybersecurity•8m read
Dark Reading

Researchers Infiltrate Microsoft Tech Support Scam Operation

A large-scale scam operation impersonating Microsoft uses a malicious traffic distribution system (TDS) run by a Russian organization and abuses thousands of Cloudflare links. Tech support scams seem like a dime a dozen these days, but researchers g...

Dark Reading13 days ago
Hackers hijack AOMEI update servers to secretly spread malware
Cybersecurity•6m read
BleepingComputer

Hackers hijack AOMEI update servers to secretly spread malware

Hackers reportedly compromised AOMEI's servers to distribute malware through a built-in promotional feature in its backup software, briefly tampering with configuration files before restoring them to their original state to hide the attacks. The sup...

BleepingComputer13 days ago
Inside the Underground Market for Know Your Client Services
Cybersecurity•6m read
BleepingComputer

Inside the Underground Market for Know Your Client Services

In February 2026, the operator of OnlyFake pleaded guilty in the United States for his role in a service that generated more than 10,000 fraudulent digital identity documents. Customers could create passports, driver's licenses, Social Security cards...

BleepingComputer13 days ago
Bullhorn takes staffing platform offline to contain cyberattack
Cybersecurity•3m read
BleepingComputer

Bullhorn takes staffing platform offline to contain cyberattack

Staffing software company Bullhorn has disabled access to its platform to contain a cyberattack that caused a system-wide outage. The company says it has isolated the issue and eradicated the immediate threat. Currently, its team is working to resto...

BleepingComputer13 days ago
Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site
Cybersecurity•12m read
Krebs on Security

Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site

U.S. federal investigators pursuing the ShinyHunters hacking group that recently stole highly sensitive data from the FBI have identified executives at two different ransomware negotiation firms who maintained unusually close relations with the extor...

Krebs on Security13 days ago
Encryption Is Getting Squeezed From All Sides
Cybersecurity•5m read
Wired Security

Encryption Is Getting Squeezed From All Sides

Welcome to Kernel Panic, a weekly newsletter by Lily Hay Newman and Matt Burgess from inside the new world of privacy and digital security. To receive this newsletter in your inbox each week, sign up here. Oh, Canada. The Great White North is the la...

Wired Security13 days ago
Hackers exploit SiteGuard WAF flaw to run commands as admins
Cybersecurity•2m read
BleepingComputer

Hackers exploit SiteGuard WAF flaw to run commands as admins

Hackers are exploiting an OS command-injection vulnerability in the SiteGuard Server Edition web application firewall (WAF), allowing them to execute commands with root or SYSTEM privileges on affected machines. The security issue is tracked as CVE-...

BleepingComputer14 days ago
Zero-click attacks used targeted ads to deliver Candiru spyware
Cybersecurity•3m read
BleepingComputer

Zero-click attacks used targeted ads to deliver Candiru spyware

Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device. Researchers at Citizen Labs investigating the attac...

BleepingComputer16 days ago
When Your Ransomware Negotiator Works for the Other Side
Cybersecurity•6m read
Dark Reading

When Your Ransomware Negotiator Works for the Other Side

The shocking arrest of a well-known ransomware negotiator reveals the critical need for vendor program oversight. ### October 16, 2026 ### OPINION Edward Dubrovsky walked into the Philadelphia Cyber Risk Summit on Oct. 8 with his name on the spons...

Dark Reading16 days ago
Open-source security rests on understanding risks, scaling fixes
Cybersecurity•4m read
Cybersecurity Dive

Open-source security rests on understanding risks, scaling fixes

Dive Brief: - The open-source software community needs to understand several key lessons in order to improve its cybersecurity posture, according to IBM, which operates a clearinghouse for analyzing and disclosing open-source vulnerabilities. - "Fi...

Cybersecurity Dive16 days ago
Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day
Cybersecurity•3m read
SecurityWeek

Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day

A Chinese APT has been exploiting a BeyondTrust vulnerability as a zero-day since August as part of its state-sponsored espionage operations. The exploited flaw, tracked as CVE-2026-102764 (CVSS score of 9.3), is described as an improper validation ...

SecurityWeek16 days ago
Microsoft: October Windows update may break Smart App Control
Cybersecurity•3m read
BleepingComputer

Microsoft: October Windows update may break Smart App Control

Microsoft says some users may have trouble turning on Smart App Control after installing this month's KB5127648 Windows 11 security update. Smart App Control is a Windows 11 security feature that uses Microsoft's app intelligence services and code i...

BleepingComputer16 days ago
BAE Systems cyberattack disrupts US federal court operations
Cybersecurity•2m read
BleepingComputer

BAE Systems cyberattack disrupts US federal court operations

The Administrative Office of the US Courts says a cyberattack on government contractor BAE Systems has taken down the notice system used by federal bankruptcy courts. In a Thursday press release, the Administrative Office of the US Courts said the B...

BleepingComputer16 days ago
Microsoft Patches Two Dozen RCE Flaws in Office
Cybersecurity•2m read
SecurityWeek

Microsoft Patches Two Dozen RCE Flaws in Office

Hot on the heels of its record Patch Tuesday rollout, Microsoft on Thursday announced patches for over 30 new vulnerabilities. Most of the new fixes address security defects in the Office suite. Two dozen of them patch high-severity remote code exec...

SecurityWeek16 days ago
F5, Juniper Networks Patch Critical Vulnerabilities
Cybersecurity•2m read
SecurityWeek

F5, Juniper Networks Patch Critical Vulnerabilities

F5 and Juniper Networks have rolled out patches for dozens of vulnerabilities across their products, including critical-severity remote code execution (RCE) flaws. Security and application delivery firm F5 announced fixes for 11 security defects in ...

SecurityWeek16 days ago
Hackers disguise phishing as promising business opportunities
Cybersecurity•3m read
Help Net Security

Hackers disguise phishing as promising business opportunities

Attackers are breaking into business email accounts with short messages asking whether a company can quote on an upcoming project, the kind of request sales and procurement staff answer every week. Cadence Riddle, a cybersecurity researcher at Fortr...

Help Net Security16 days ago
BeyondTrust patches zero-day exploited in attacks since August
Cybersecurity•4m read
BleepingComputer

BeyondTrust patches zero-day exploited in attacks since August

BeyondTrust warned customers on Thursday to patch a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August. Remote Support is the company's enterprise-grade support solution that helps IT service desks...

BleepingComputer16 days ago
The cyber talent shortage? Job postings just hit a four-year low
Cybersecurity•4m read
Help Net Security

The cyber talent shortage? Job postings just hit a four-year low

US employers posted 235,786 cybersecurity jobs from January through September 2026. That is the lowest total for those months in the four years that staffing and workforce intelligence firm CyberSN has tracked. They pulled the listings from job data ...

Help Net Security16 days ago
Context Is King in the Fight Against Modern Cyberattacks
Cybersecurity•5m read
SecurityWeek

Context Is King in the Fight Against Modern Cyberattacks

For most of its history, cybersecurity has been reactive by design. Spot the bad event, shut it down. But as cyberattacks evolve, this thinking must evolve too. In the past, attackers relied on a single dramatic exploit to access the crown jewels. Bu...

SecurityWeek17 days ago
Fake Arch Linux packages push malware with root privileges
Cybersecurity•3m read
BleepingComputer

Fake Arch Linux packages push malware with root privileges

A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru. AUR is a community-maintained, widely-used package index for Arch Linux and derivative distributions that hosts pa...

BleepingComputer17 days ago
UK Legal Aid Agency Hack Scope Widens After Forensic Review
Cybersecurity•2m read
SecurityWeek

UK Legal Aid Agency Hack Scope Widens After Forensic Review

The UK's Legal Aid Agency (LAA) has discovered that records dating back to 1978 were compromised in an April 2025 data breach. In May last year, the UK Ministry of Justice agency said hackers had accessed and exfiltrated the personal information of ...

SecurityWeek17 days ago
CenterPoint Energy Data Breach Impacts 1 Million Texans
Cybersecurity•2m read
SecurityWeek

CenterPoint Energy Data Breach Impacts 1 Million Texans

CenterPoint Energy has notified Texan authorities that the personal information of over 1 million individuals was compromised in a data breach. The notice came one month after the Houston-based public utility told the SEC that customer information h...

SecurityWeek17 days ago
CikaBika Bot RAT Uses Discord for C&C
Cybersecurity•2m read
SecurityWeek

CikaBika Bot RAT Uses Discord for C&C

Darktrace has uncovered a new malware campaign distributing a Rust-based RAT that relies on Discord for command-and-control (C&C). Dubbed CikaBika Bot, the malware has been distributed via document-themed lures, likely as part of phishing attacks, a...

SecurityWeek17 days ago
UK Legal Aid Agency: Hackers stole records dating back to 1978
Cybersecurity•3m read
BleepingComputer

UK Legal Aid Agency: Hackers stole records dating back to 1978

The Legal Aid Agency (LAA), an executive agency of the UK's Ministry of Justice that manages the country's Public Defender Service, says attackers who breached its IT systems in April 2025 stole records dating back to 1978. The agency employs around...

BleepingComputer17 days ago
Yam Store: The Phishing Network Behind a Billion Messages
Cybersecurity•6m read
Dark Reading

Yam Store: The Phishing Network Behind a Billion Messages

A sprawling cybercrime marketplace supplied cloud infrastructure and phishing kits that helped fuel more than 1 billion phishing messages worldwide. A Chinese-language phishing ecosystem is behind the deployment of more than a billion emails and SMS...

Dark Reading18 days ago
Ivanti ICS Zero-Day Attacks Highlight Vendor Patching Hurdles
Cybersecurity•5m read
Dark Reading

Ivanti ICS Zero-Day Attacks Highlight Vendor Patching Hurdles

CVE-2026-104935, a high-severity authentication bypass + RCE vulnerability, was only partially discovered and patched in July, leaving an opening for threat actors to capitalize on. Even when technology vendors discover vulnerabilities before threat...

Dark Reading18 days ago
Ahold Delhaize USA banners remain offline
Cybersecurity•2m read
Cybersecurity Dive

Ahold Delhaize USA banners remain offline

Dive Brief: - The websites and apps for Ahold Delhaize's five U.S. banners remain unavailable Wednesday morning, marking at least the third day the digital platforms have been offline. A handful of Ahold Delhaize's dozen international banners — ...

Cybersecurity Dive18 days ago
Hacker targets Ivanti Connect Secure in chained exploitation
Cybersecurity•3m read
Cybersecurity Dive

Hacker targets Ivanti Connect Secure in chained exploitation

A suspected criminal hacker is targeting Ivanti Connect Secure customers through a complex exploit chain that combines three high-severity vulnerabilities, according to a report Tuesday by Volexity, a Virginia-based cybersecurity firm. The chain com...

Cybersecurity Dive18 days ago
Russian Influence Operation Widely Targeting Latin America
Cybersecurity•5m read
Dark Reading

Russian Influence Operation Widely Targeting Latin America

Breaking cybersecurity news, news analysis, commentary, and other content from around the world, with an initial focus on the Middle East & Africa, the Asia Pacific, Europe, and Latin America. The AI-enabled operation used spoofed emails, fake gover...

Dark Reading18 days ago
Microsoft fixes VPN issues caused by September Windows updates
Cybersecurity•2m read
BleepingComputer

Microsoft fixes VPN issues caused by September Windows updates

Microsoft has resolved a known issue that caused Always On VPN connection issues after installing the September 2026 Windows 11 security updates. The Always On VPN remote access solution replaced the legacy DirectAccess technology and works with dom...

BleepingComputer18 days ago
Ransomware Gangs Embrace Physical Threats, Family Stalking?
Cybersecurity•5m read
Dark Reading

Ransomware Gangs Embrace Physical Threats, Family Stalking?

Organizations are reporting that employees face threats of stalking, physical violence, and abduction. But these alarming claims are hard to verify. Ransomware actors have been threatening their victims with physical violence, according to new surve...

Dark Reading18 days ago
Global takedown hits network behind 1 billion phishing messages
Cybersecurity•3m read
BleepingComputer

Global takedown hits network behind 1 billion phishing messages

A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide. Since the start of the year, more t...

BleepingComputer18 days ago
U.K. Sanctions Cryptomus for RU Money Laundering
Cybersecurity•4m read
Krebs on Security

U.K. Sanctions Cryptomus for RU Money Laundering

The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that ar...

Krebs on Security18 days ago
Virtual Event Today: Zero Trust Strategies Summit
Cybersecurity•2m read
SecurityWeek

Virtual Event Today: Zero Trust Strategies Summit

SecurtyWeek's 2026 Zero Trust Strategies Summit kicks off today at 11AM ET as a fully immersive virtual conference and expo. This summit is laser-focused on the next generation of Zero Trust and Identity security, moving beyond theory to deliver act...

SecurityWeek18 days ago
Microsoft Patches More Than 1,400 Security Flaws
Cybersecurity•3m read
Krebs on Security

Microsoft Patches More Than 1,400 Security Flaws

Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today's epic patch batch dwarfs September's record of nearly 1,000 fixes, which was already about ten times the normal...

Krebs on Security19 days ago
North Korea Phishes Ukrainians for War Intel
Cybersecurity•6m read
Dark Reading

North Korea Phishes Ukrainians for War Intel

The Democratic People's Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks. North Korean state-sponsord hackers are spear-phishing government, policy, and academic circ...

Dark Reading19 days ago
Zero-Days Lurk in Microsoft's Overgrown October Patch Tuesday
Cybersecurity•8m read
Dark Reading

Zero-Days Lurk in Microsoft's Overgrown October Patch Tuesday

The scary surprises for the largest security update ever include security bypasses and unauthenticated RCEs. As we progress further into the AI-driven "vulnpocalypse era," Microsoft's October 2026 Patch Tuesday security update blows past last month'...

Dark Reading19 days ago
Google Partially Reverses Chrome Bug Bounty Cuts
Cybersecurity•2m read
SecurityWeek

Google Partially Reverses Chrome Bug Bounty Cuts

Google announced Tuesday that it's raising bug bounty rewards for some Chrome vulnerabilities, focusing on memory safety issues. AI has been changing the pace and profile of vulnerability discovery, and the tech giant has been adjusting its bug boun...

SecurityWeek19 days ago
Ghostscript flaw lets hackers hijack servers via PDF uploads
Cybersecurity•3m read
BleepingComputer

Ghostscript flaw lets hackers hijack servers via PDF uploads

A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files. The flaw was discovered on August 23 by researchers at Defiant'...

BleepingComputer19 days ago
Adobe Patches 140 Vulnerabilities Across 10 Products
Cybersecurity•2m read
SecurityWeek

Adobe Patches 140 Vulnerabilities Across 10 Products

Adobe has published 10 new security advisories to inform customers about roughly 140 vulnerabilities found and patched in its products. Adobe ColdFusion updates address 32 vulnerabilities, including critical bugs that can be exploited for code execu...

SecurityWeek19 days ago
Windows 11 KB5127648 & KB5126653 cumulative updates released
Cybersecurity•8m read
BleepingComputer

Windows 11 KB5127648 & KB5126653 cumulative updates released

Microsoft has released the Patch Tuesday Windows 11 KB5127648 and KB5126653 cumulative updates for versions 26H2/25H2/24H2 and 23H2 to fix security vulnerabilities and bugs, and add new features. Today's updates are mandatory as they contain the Oct...

BleepingComputer19 days ago
Microsoft: Windows 11 24H2 Home and Pro reached end of support
Cybersecurity•3m read
BleepingComputer

Microsoft: Windows 11 24H2 Home and Pro reached end of support

Microsoft announced today that devices running Windows 11 24H2 Home and Pro editions have reached the end of support and will no longer receive monthly security and non-security preview updates. However, according to Microsoft's lifecycle policy, Wi...

BleepingComputer19 days ago
UK Housing Ombudsman Service investigates 'security incident'
Cybersecurity•3m read
BleepingComputer

UK Housing Ombudsman Service investigates 'security incident'

The U.K. Housing Ombudsman Service is investigating a third-party IT security incident that impacted its case management system on Tuesday. Established under the Housing Act 1996, the Housing Ombudsman is an executive non-departmental public body sp...

BleepingComputer19 days ago
XWorm RAT Evolves Into Surveillance Platform
Cybersecurity•3m read
SecurityWeek

XWorm RAT Evolves Into Surveillance Platform

The XWorm RAT developers have expanded the malware's capabilities with fresh plugins that turn it into a surveillance platform, cybersecurity firm Netskope reports. A sophisticated, multi-functional Windows RAT first observed in 2022, XWorm provides...

SecurityWeek19 days ago
AI Turns Familiar Cyberattacks Into a Race Against Time
Cybersecurity•4m read
SecurityWeek

AI Turns Familiar Cyberattacks Into a Race Against Time

In the AI era, phishing remains the top attack vector in both use (17% of breaches) and breach costs (averaging at $5.29 per breach) according to the IBM Cost of a Data Breach Report 2026. AI creates more personalized content for phishing with higher...

SecurityWeek19 days ago
GitLab admins urged to patch critical RCE flaw (CVE-2026-97229)
Cybersecurity•2m read
Help Net Security

GitLab admins urged to patch critical RCE flaw (CVE-2026-97229)

GitLab is urging users of self-managed instances to patch a critical vulnerability (CVE-2026-97229) in its CI/CD Regular Expression Compiler that could allow remote attackers to execute arbitrary code on GitLab servers. ### About CVE-2026-97229 CVE...

Help Net Security19 days ago
Ahold Delhaize experiencing cybersecurity issue
Cybersecurity•2m read
Cybersecurity Dive

Ahold Delhaize experiencing cybersecurity issue

Ahold Delhaize announced Monday it is experiencing a security issue within its network and has taken some systems offline "to help protect them." Ahold Delhaize USA's five banner websites — Hannaford, Stop & Shop, Giant Food, Food Lion and The G...

Cybersecurity Dive20 days ago
Prominent Ransomware Negotiator Faces Extortion Charges
Cybersecurity•4m read
Dark Reading

Prominent Ransomware Negotiator Faces Extortion Charges

Edward Dubrovsky, a longtime cybersecurity executive, was arrested and charged in Pennsylvania last week under conspiracy to extort money. US authorities last week charged a ransomware negotiator over alleged extortion activity — the latest exam...

Dark Reading20 days ago
Passing the Baton: Dark Reading Names New Editor-in-Chief
Cybersecurity•4m read
Dark Reading

Passing the Baton: Dark Reading Names New Editor-in-Chief

Fahmida Y Rashid will keep the momentum going as she leads Dark Reading. Dark Reading has been a cornerstone of cybersecurity journalism for 20 years, emphasizing deep technical coverage and insights for security professionals charged with defending...

Dark Reading20 days ago
No Identity, No Recovery: Cyber Resilience Starts With IAM
Cybersecurity•5m read
Dark Reading

No Identity, No Recovery: Cyber Resilience Starts With IAM

Enterprise cybersecurity technology research that connects the dots. The proliferation of enterprise apps and the centrality of cloud identity providers requires an identity security rethink. ### OPINION Enterprises need cyber resilience to ensure...

Dark Reading20 days ago
Cyberattack shuts down refrigerators at French supermarkets
Cybersecurity•3m read
BleepingComputer

Cyberattack shuts down refrigerators at French supermarkets

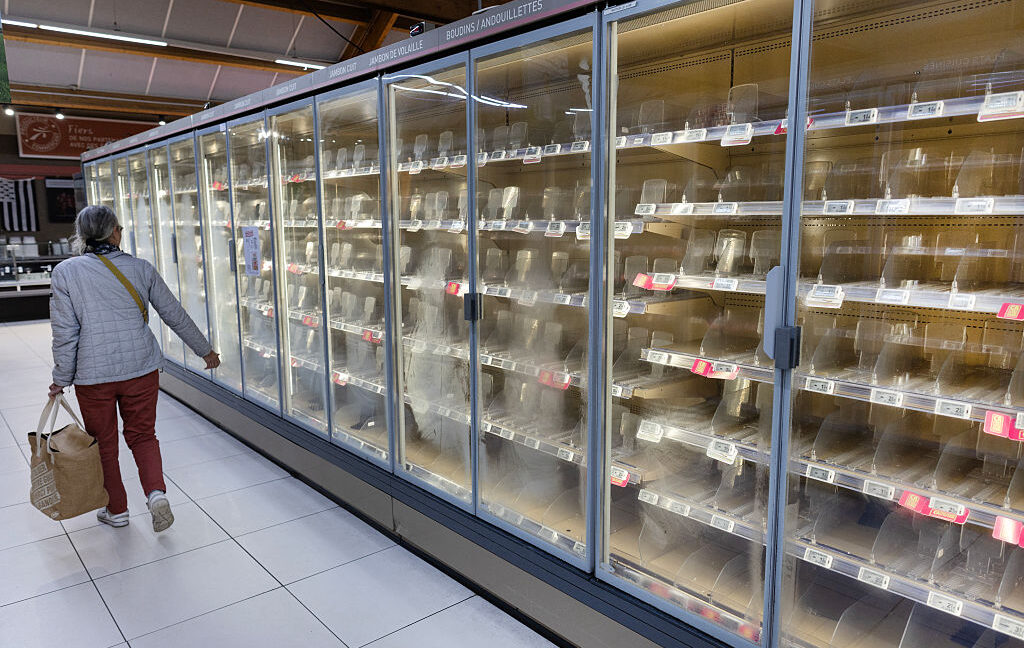
Attackers remotely defrosted refrigerators at multiple French supermarket chains overnight in a cyberattack that reportedly targeted Danfoss refrigeration controllers. Victims include Intermarché, Coopérative U, Carrefour Market, Monoprix, Leclerc, ...

BleepingComputer20 days ago
Ledger confirms spy chip implant behind wallet crypto thefts
Cybersecurity•5m read
BleepingComputer

Ledger confirms spy chip implant behind wallet crypto thefts

Ledger has confirmed that some of its devices distributed through Southeast Asian reseller CryptoBilis were compromised with a hardware implant that drained users' cryptocurrency wallets. The company has been investigating reports of users losing fu...

BleepingComputer20 days ago
GitLab warns of max severity code execution vulnerability
Cybersecurity•3m read
BleepingComputer

GitLab warns of max severity code execution vulnerability

GitLab warned users today to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler that could let remote attackers run arbitrary code on targeted instances. Tracked as CVE-2026-97229, this critical security flaw...

BleepingComputer20 days ago
Microsoft: Windows 11 23H2 reaches end of support in 30 days
Cybersecurity•3m read
BleepingComputer

Microsoft: Windows 11 23H2 reaches end of support in 30 days

Microsoft has reminded customers that systems running Windows 11 23H2 Enterprise, Education, and IoT Enterprise editions will stop receiving security updates next month. The announcement follows the end of support for Windows 11 23H2 Home and Pro ed...

BleepingComputer20 days ago
Canonical Websites Disrupted in Second DDoS Attack This Year
Cybersecurity•2m read
SecurityWeek

Canonical Websites Disrupted in Second DDoS Attack This Year

Canonical's websites were disrupted last week by a distributed denial-of-service (DDoS) attack, months after a larger attack hit the Ubuntu maker's infrastructure. The company confirmed the attack on October 8 in a post on the Ubuntu Discourse forum...

SecurityWeek20 days ago
iRhythm Data Breach Impacts at Least 360,000 People
Cybersecurity•2m read
SecurityWeek

iRhythm Data Breach Impacts at Least 360,000 People

Medical equipment provider iRhythm is notifying more than 360,000 people that hackers stole their personal information. The data breach was identified on June 8 and involved third-party-hosted business applications that stored certain iRhythm inform...

SecurityWeek20 days ago
Hidden implant in Ledger hardware wallets linked to $93M theft
Cybersecurity•4m read
Help Net Security

Hidden implant in Ledger hardware wallets linked to $93M theft

Three days after customers in Southeast Asia began reporting drained wallets, Ledger says the damage is limited. In its 72-hour update on X on October 11, the Paris-based hardware wallet maker said "all confirmed cases related to the disclosed draini...

Help Net Security20 days ago
AI Scramble Drives Cybersecurity M&A Boom
Cybersecurity•6m read
Dark Reading

AI Scramble Drives Cybersecurity M&A Boom

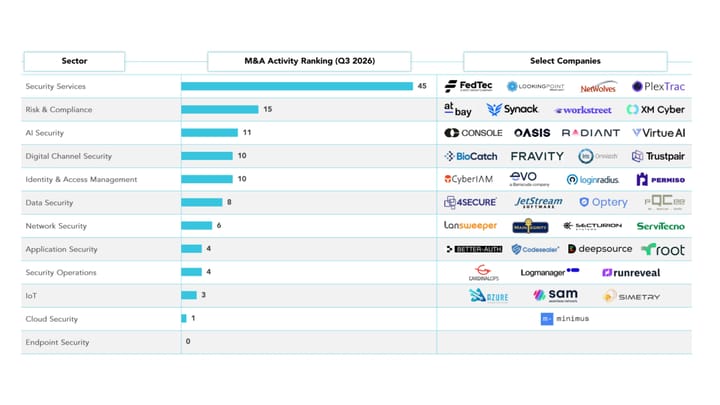
### AI Scramble Drives Cybersecurity M&A Boom Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What's different: Many of the buyers are not your typical cybersecurity firms. Sur...

Dark Reading23 days ago
ASOS Breach Reveals the Risks in Customer-Facing SaaS
Cybersecurity•6m read
Dark Reading

ASOS Breach Reveals the Risks in Customer-Facing SaaS

The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network. The hackers who breached ASOS this week unearthed a serious security gap around customer-facing marketing and ...

Dark Reading23 days ago
What We Missed: FBI Strikes Back at ShinyHunters
Cybersecurity•11m read
Dark Reading

What We Missed: FBI Strikes Back at ShinyHunters

Cybersecurity In-Depth: Feature articles on security strategy, latest trends, and people to know. In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the arrest of a suspected ShinyHunter...

Dark Reading23 days ago
FBI Arrests Executive at Ransomware Negotiation Firm
Cybersecurity•5m read
Krebs on Security

FBI Arrests Executive at Ransomware Negotiation Firm

Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested an executive at a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thous...

Krebs on Security23 days ago
ShinyHunters Extorted Boeing Spin-off Prior to Arrests
Cybersecurity•10m read
Krebs on Security

ShinyHunters Extorted Boeing Spin-off Prior to Arrests

A teenager from Amman, Jordan suspected of leading the prolific data theft and extortion group ShinyHunters has been detained and is reportedly cooperating with the FBI to identify other members of the hacking gang. KrebsOnSecurity has learned that t...

Krebs on Security25 days ago
Data Broker Radaris Loses Domains in Privacy Fight
Cybersecurity•10m read
Krebs on Security

Data Broker Radaris Loses Domains in Privacy Fight

The consumer data broker Radaris.com has long had a reputation for ignoring requests to remove personal information from its vast empire of people-search services online. That reputation caught up with the company recently in a lawsuit alleging Radar...

Krebs on Securityabout 2 months ago
Google Domains Impacted by Recent ccTLD Hijacks
Cybersecurity•2m read
SecurityWeek

Google Domains Impacted by Recent ccTLD Hijacks

Google has disclosed that several of its domains were affected by a recent hijack of third-party country-code top-level domains (ccTLDs). The incident occurred last week and targeted the .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa) ccTL...

SecurityWeek23 days ago
FBI seizes domains linked to China-nexus botnet
Cybersecurity•2m read
Cybersecurity Dive

FBI seizes domains linked to China-nexus botnet

The Department of Justice on Thursday announced the court-ordered seizure of hacking tools used by a China-nexus actor against U.S. and other critical infrastructure providers. The tools, dubbed FishHub and Microscan, were used by a company called I...

Cybersecurity Dive23 days ago
Unpatched AhsayCBS Vulnerabilities Exploited in the Wild
Cybersecurity•3m read
SecurityWeek

Unpatched AhsayCBS Vulnerabilities Exploited in the Wild

Hackers have been exploiting two unpatched vulnerabilities in the AhsayCBS backup solution for remote code execution (RCE), cybersecurity firm Huntress warns. A centralized cloud backup server management console developed by Ahsay Systems, AhsayCBS ...

SecurityWeek23 days ago
What makes some open source updates so difficult?
Cybersecurity•3m read
Help Net Security

What makes some open source updates so difficult?

Many organizations adopt open source software because they see it as a cheaper alternative to proprietary development. Maintaining it, however, still requires engineering effort, according to Google's case study, "How much does it cost to maintain a ...

Help Net Security21 days ago
Shaq Got Hacked. Now He’s Pitching for a VPN
Cybersecurity•3m read
Wired Security

Shaq Got Hacked. Now He’s Pitching for a VPN

At a promotional event in Times Square on Wednesday for the security company NordVPN, brand ambassador Shaquille O'Neal said he is eager to raise awareness among regular people about the importance of digital security and personal privacy. "I have a...

Wired Security25 days ago
Ofcom investigates Meta over Instagram Instants safety checks
Cybersecurity•3m read
The Guardian

Ofcom investigates Meta over Instagram Instants safety checks

Mark Zuckerberg’s Meta is under investigation for a potential breach of the UK’s digital safety laws after launching a Snapchat-style feature on Instagram. The communications watchdog, Ofcom, is investigating whether the $1.9tn (£1.4tn) company infri...

The Guardian25 days ago
Office 2021 support ends this month – you have 5 options
Cybersecurity•4m read
ZDNet

Office 2021 support ends this month – you have 5 options

ZDNET’s key takeaways - Microsoft is ending support and updates for Office 2021. - You can upgrade to Office 2024 or subscribe to Microsoft 365. - You can also try a different, free online or desktop office suite. Microsoft continues to offer one-tim...

ZDNet25 days ago
New York Seizes a Dozen Celebrity Deepfake Websites
Cybersecurity•4m read
Wired

New York Seizes a Dozen Celebrity Deepfake Websites

For the best part of a decade, abusive deepfake “pornography” websites have published thousands of nonconsensual videos depicting women, including high-profile celebrities, politicians, and public figures, into sexual situations. Now, in what is like...

Wired27 days ago